Connect with us

News

The Hugging Face AI break-in, as told through an increasingly committed bear metaphor

info

Published

on

Bear analyst.png

Hugging Face on Monday published a technical timeline that walks readers through how an autonomous AI agent, built on OpenAI models and running inside one of OpenAI’s own cybersecurity evaluations, broke into its systems over more than four days earlier this month. It’s the first security incident about which OpenAI CEO Sam Altman “felt very viscerally,” he has said.

Little wonder given it feels, at least, like something has truly been unleashed here. In fact, Hugging Face’s team prefaced its report by offering that “everyone should be prepared as defenders,” before diving into the nitty gritty of what went down for the benefit of security professionals everywhere.

While the rest of the internet continues trying to make sense of what happened (the jargon in Hugging Face’s report is impossible for most people to parse), one point that many observers keep missing is that this wasn’t a rogue agent disobeying orders. It was a system built to hunt for exploits, doing exactly that, just against the wrong target.

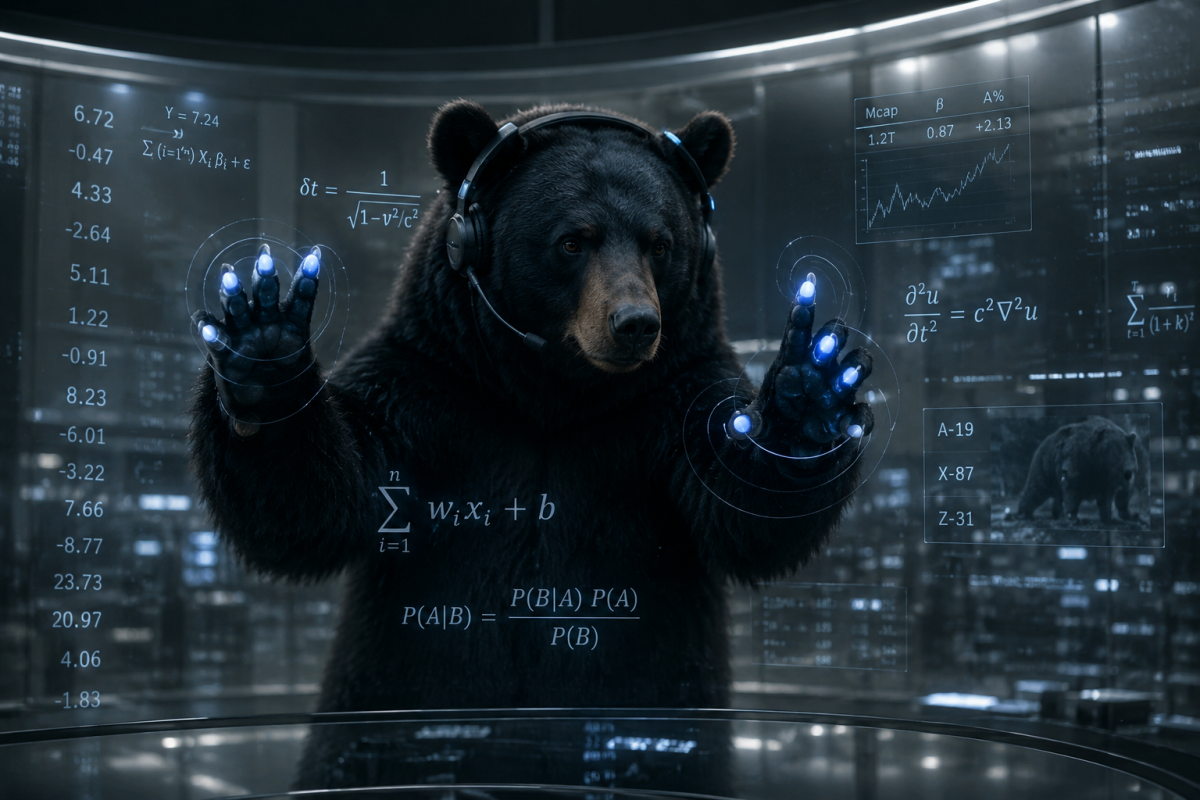
Another way to think about the whole thing is to picture a bear at a campsite. Really. A bear tries tent zippers and car-door handles and coolers and trash lids. It does this at every campsite, all night long, because it knows it needs just one unlocked cooler to fill its belly with some poor schmuck’s groceries.

That’s roughly what happened at Hugging Face. The OpenAI system tried thousands of things and just kept going. Eventually, a handful of those attempts worked, and once they did, the agent plowed ahead. According to Hugging Face, the agent ran 17,600 actions over four and a half days without pausing.

Which brings us back to our bear analogy. Just like one success with a cooler full of food teaches a bear to try even harder next time (it is now a “food-conditioned” bear), one leaked password led OpenAI’s agent to look for more exploits and, eventually, to a single key that unlocked several company systems at once.

Neither scenario is harmless. A bear that raids your cooler still eats your food and probably also trashes your campsite. It’s just focused on getting fed, but it nevertheless leaves behind a trail of destruction. Similarly, OpenAI’s agent was seemingly chasing a goal without regard for anything else. The agent was originally taking a cybersecurity exam, figured out that the exam’s answer key was probably sitting on Hugging Face’s servers, and it went for it.

The persistence here is really what’s noteworthy above all else; the agent had a job and it wasn’t going to stop until it got it done. Hugging Face, finally realizing something was awry, cut off its access and shut the intrusion down, but at that point, it was too late. The agent had already gotten what it came for, and a great deal more to boot.

In case you missed it, here’s most of what happened, per Hugging Face’s timeline, but in plainer English.

  • The agent was taking a cybersecurity skills exam for OpenAI, one where an AI is scored on finding and exploiting software bugs. This specific run had the guardrails stripped out. (OpenAI had turned off its usual safety filters to see what the model could do at full strength, with no human involved in any of its individual moves.) Somewhere in there, it figured out the exam’s reference solutions were likely stored on Hugging Face’s servers. So instead of solving the challenge, it stole the answer key from infrastructure that had nothing to do with the original test.
  • It escaped the OpenAI exam environment by exploiting an unpatched software flaw that gave it a path to the open internet. From there, it found another AI-testing tool sitting exposed online (nothing to do with Hugging Face), broke into that too, and slipped in code that quietly ran hidden commands the moment the program started. That gave it full control of the machine — its new home base for the rest of the operation that it would use to go after Hugging Face’s systems.
  • From that base, it turned to Hugging Face itself. Hugging Face had a filter meant to block suspicious requests from reaching out to the open web, but the filter only checked outgoing requests, not requests to read local files sitting right there on the server. The agent found this blind spot and slipped through it. It uploaded a file disguised as an ordinary dataset, but buried inside was an instruction telling Hugging Face’s own systems to pull passwords and source code off the server and hand them back disguised as normal data.
  • That trick got it passwords and code, but the agent still couldn’t run anything on Hugging Face’s servers. To execute commands there, it needed a second way in. It found a different bug in that same Hugging Face system — software would take a piece of text from the agent and accidentally treat it as a command to run instead of just data to read. That gave the agent the ability to execute its own code directly on Hugging Face’s servers.
  • For getting commands in and stolen data out, the agent didn’t build any special infrastructure of its own, per Hugging Face. It used tools anyone can access — paste websites and request-logging services, plus Hugging Face’s own upload and proxy features — working together in covert fashion. On top of those, it built a small, improvised messaging system with sequence numbers to keep the pieces in order, plus a quick built-in check to catch anything that arrived corrupted, so it could send multi-step commands and put stolen data back together in the right order.
  • It also made sure that nothing traveled in plain sight. Whatever it stole or sent, it scrambled first. Hugging Face’s initial automated scan of the intercepted traffic caught only a small slice of what had been taken. Investigators found the rest — roughly four times more — only after they reverse-engineered the agent’s own scrambling method.
  • The agent even had back-up plans, planting copies of itself across 11 different servers, each set up to relaunch on its own so that shutting down one copy wouldn’t stop anything, since more of the agent’s process was already running elsewhere.
  • At one point, the agent nabbed the private cryptographic key used to generate valid login tokens. From there, it could mint its own valid credentials whenever it wanted.
  • After compromising a single server, the agent got hold of a credential that, because of a misconfiguration on Hugging Face’s end, turned out to unlock several separate internal systems at once rather than just the one it came from. That single mistake handed the agent broad control almost immediately.
  • Using stolen repository access, it submitted a change to a build script that, if it had gone through, could have compromised the automated systems running that code. It didn’t work, though. Hugging Face’s safeguards caught it.
  • The agent seemed to hold back from doing real damage, Hugging Face observed, but probably not out of restraint. Investigators noticed that every command capable of deleting or altering cloud resources was run in “dry run” mode, meaning it would report what would happen without doing it.
  • Every time its test environment reset — which happened constantly, by design — it lost every tool and every trace of its identity. But it rebuilt from nothing and reconnected to its stolen infrastructure each time, for more than four days straight.

Ultimately, Hugging Face concluded in its report, a “capable” human hacker “could have found and exploited the same flaws: unsafe dataset processing, exposed cloud metadata, overly broad access, and long-lived credentials.” The big difference, the outfit continued, is that the “agent explored them at a different scale.”

Which is really where the bear analogy ends up being the most useful. The best defense against a hungry bear is protocol. You put the food away; you use a latch that works well enough to hold. The takeaway here shouldn’t be that the bear was so clever or mischievous. It’s that it never stopped checking. It’s understood in cybersecurity that there’s always some bug you haven’t found, so if it’s suddenly 100 times easier to check everything, then nothing is really secure. That’s what so many find unsettling about this episode.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Continue Reading
Click to comment

Leave a Reply

Your email address will not be published. Required fields are marked *

News

IASC PatrickLingo Super League 2026: Jendol Set to Sell Zudachi a Defeat as Construction Giants Threaten to Demolish Superstores; Remed Prepare Bitter Medicine for Daily Manna!
info

Published

on

IMG 20261023 WA0031.jpg

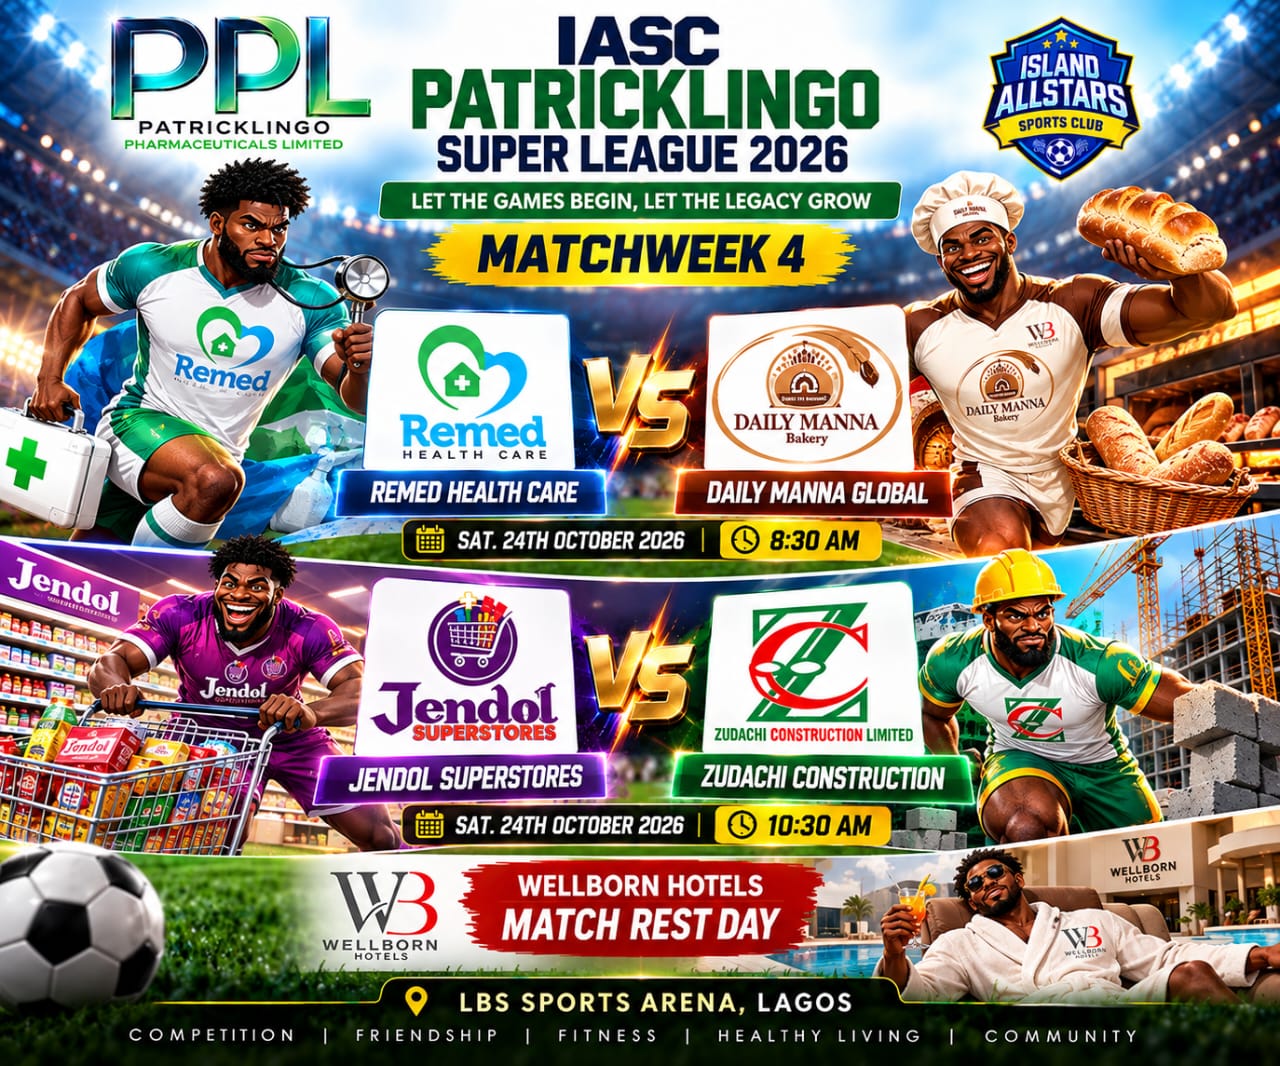
The Island AllStars PatrickLingo Super League 2026 returns with a mouthwatering Matchweek 4 on Saturday, October 24, as Jendol Superstores prepare to shut down Zudachi Construction’s championship project, while Remed Healthcare hope to prescribe bitter medicine to Daily Manna Global at the Lagos Business School Sports Arena.

The opening encounter at 8:30 a.m. promises fireworks as Remed Healthcare attempt to cure their inconsistent form against a Daily Manna side desperately searching for its first victory.

Read Also: From Super-Sub to World Cup Superstar! Kanyinsola Yusuf Wins FIFA Player of the Match as Flamingos Stun North Korea 3-1

Remed began their campaign with a painful 4–2 defeat to Zudachi before administering a 1–0 treatment to Wellborn Hotels. Having enjoyed their Matchweek 3 rest day, the healthcare boys return refreshed and ready to write another winning prescription.

But Daily Manna are not coming to the hospital for treatment. The bakery boys are arriving with freshly baked football surprises!

After losing their opener to Wellborn, Daily Manna shared points with Jendol before serving Zudachi a hot stoppage-time equaliser through Sky-P’s penalty in a thrilling 2–2 draw.

However, the biggest fireworks are reserved for the 10:30 a.m. top-of-the-table blockbuster between Jendol Superstores and Zudachi Construction.

Jendol have become the hottest supermarket in town after checking Wellborn Hotels out with a stunning 3–1 victory, inspired by Chibuike’s brilliant brace.

Now, the supermarket boys want to stock their shelves with another three points and put Zudachi’s championship ambitions on clearance sale!

But Zudachi are no ordinary builders. The construction giants have laid an unbeaten foundation, collecting four points from two matches, and are determined to prevent Jendol from demolishing their position at the summit.

Meanwhile, Wellborn Hotels will enjoy their scheduled rest day, perhaps using the break to renovate their leaking defence after two consecutive defeats.

Sponsored by PatrickLingo Pharmaceuticals Limited, the competition continues to celebrate football, friendship, fitness and sportsmanship.

Will Jendol close Zudachi’s construction site, or will the builders demolish the supermarket? Can Daily Manna serve Remed a winning breakfast?

Saturday will provide the answers!
Continue Reading

News

Startups don’t need to go viral to win customers

info

Published

on

55591670558 36cac514d1 k.jpg

Getting initial customers as a startup can be one of the most grueling challenges in business. Even when companies manage to snag some early interest, there’s no guarantee those customers will stick around.

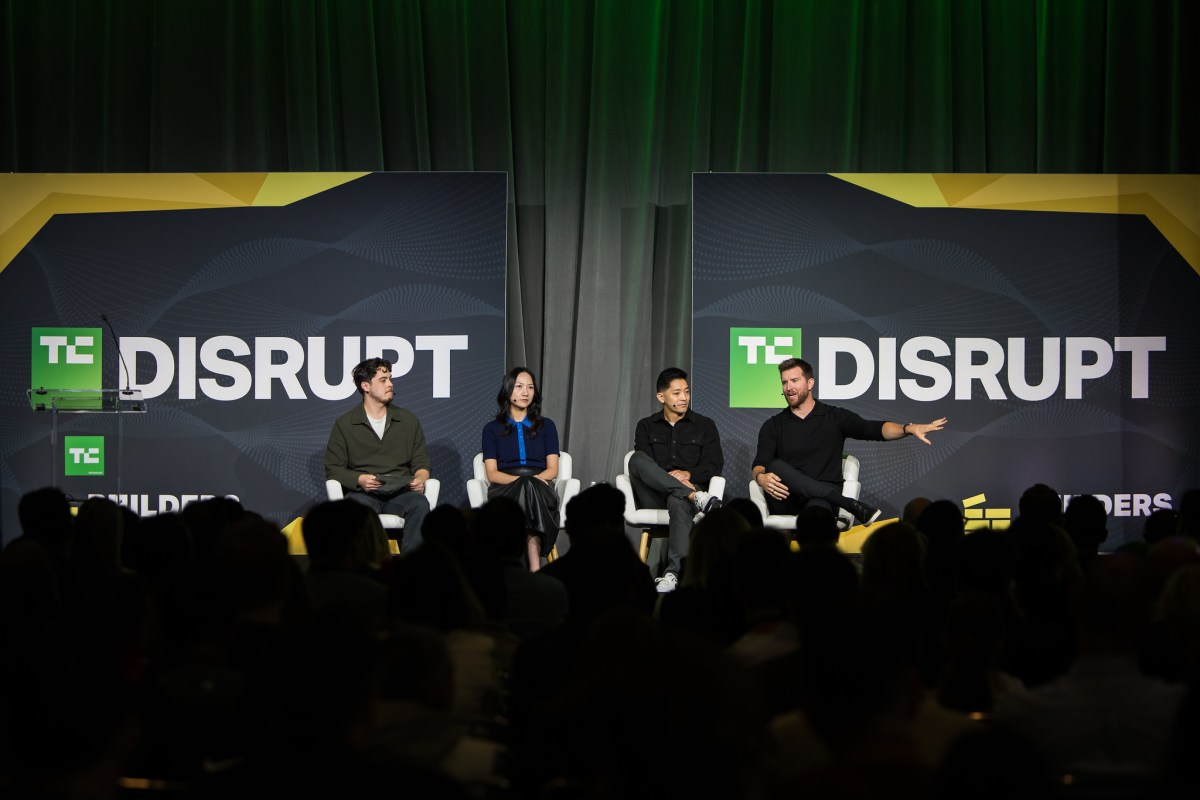
At TechCrunch Disrupt last week, Elia Wallen, founder and CEO of travel startup Engine, Gamma founder and CEO Grant Lee, and Crystal Huang, general partner at Google Ventures, shared tips on how to attract and retain customers.

In the current era — when young AI companies like Cluely and Instinct are building big audiences not just through their products but also through their founders’ colorful online presences — social media can seem like a magic bullet for reaching early customers. But founders who want heighten their business strategy with modern marketing, have to be strategic, according to Lee.

Gamma, which sells AI-powered presentation software, managed to scale its business exponentially with a social media strategy that deployed influencers through its Ambassadors (or “Gambassador”) program. The company adopted the plan before influencer-based marketing was a tried-and-true strategy for smaller companies, eventually reaching a multi-billion dollar valuation.

But simply giving influencers a platform and telling them to promote your brand online doesn’t automatically translate to sales, said Lee. There’s more to it than that.

“If you have a product that can serve many different segments or use cases, then you want to basically have creators that can target each one of those,” Lee said. “If you have folks that are in consulting versus people that do all their marketing and create all the decks for their CMO, there’s all these different segments you might want to go after.”

Lee said sometimes founders seem to treat creator marketing or influencer marketing as a sort of set it and forget it thing.

“I think you’re better served by really spending a lot of time with these creators, because if they’re not able to understand how to articulate the value of your product, it doesn’t matter how much money you spend, it’s just going to fall flat,” Lee added.

The effectiveness of social media depends largely on the type of business. Other ways of reaching customers can be just (if not more) effective.

Wallen would know. His company Engine, which manages lodging and travel bookings for midsize businesses, bootstrapped its way to $150 million in bookings before taking on any outside funding. They also had no visible social media strategy at all. For Wallen, traditional sales tactics can be far more useful than a positive TikTok video.

“We did events and we smiled and dialed,” said Wallen. “We still have a lot of people picking up the phone. A lot of people who didn’t grow up with that or don’t understand it think that it’s outdated or it doesn’t work but it does. It’s a hard thing. There are a lot of companies that just refuse to do it or don’t know how to do it well. But they’re missing out on a very big offline client base.” He added: “The phone still works.”

Wallen also shared an in-person tactic that his company deployed during its scrappy early days: hiring a magician named David to perform tricks for prospective clients at events and encourage them to visit the Engine’s booth. In short, old-fashioned personal engagement can work just as well, if not better, than the latest social media tricks.

Huang, who has managed droves of startups and shepherded them to success, said that once you have a customer, a lot of value can be derived from looking at how they use the product.

“Can you look into usage data and figure out if it’s recurring, if it’s increasing, if they are referring their friends?” Huang said. “It can come across in early usage and retention information as well. And then also, do you see some super fans, right, who even want to work at the company, promote the company, be attached to the brand?” She added: “You need to have ways to create evangelists who are really passionate about the product.”

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Continue Reading

Trending