News
Password manager Dashlane says hackers stole some customers’ password vaults




News
PLATEAU RETRAINS 353 OPERATION RAINBOW OPERATIVES, DEPLOYS VEHICLES TO STRENGTHEN SECURITY OPERATIONS

Views: 2
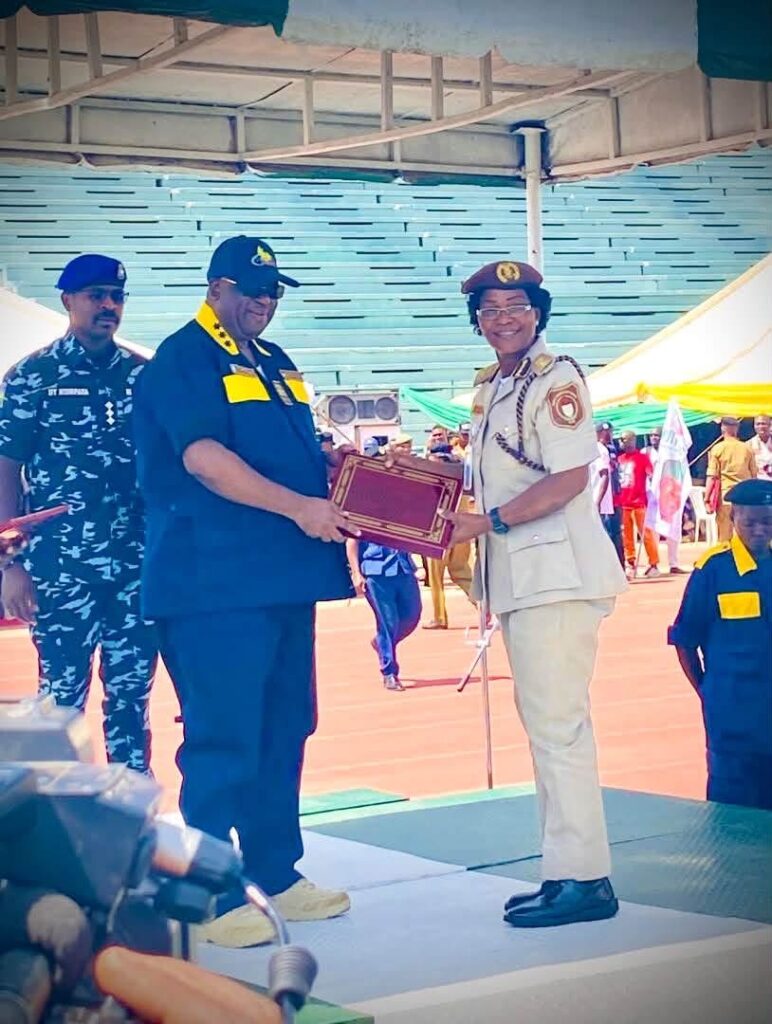
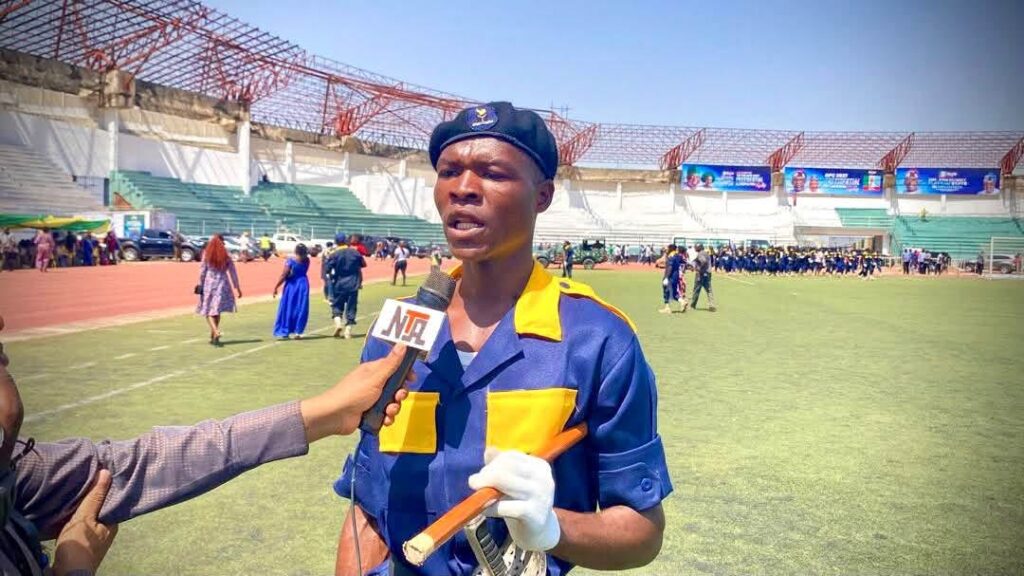
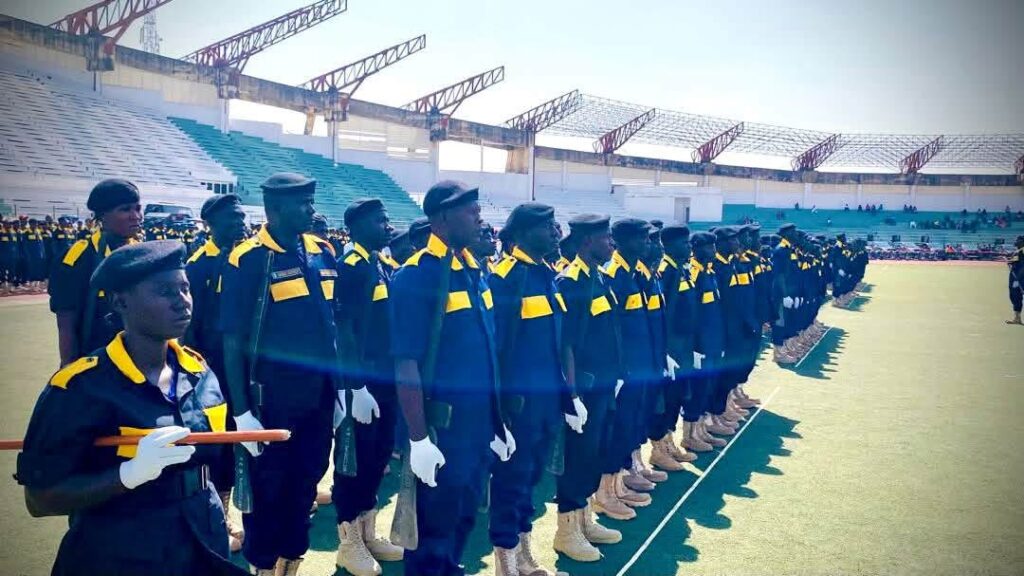
The Plateau State Government has intensified efforts to strengthen its community-based security architecture with the retraining of 353 operatives of Operation Rainbow and the provision of operational vehicles to enhance security operations across the state.
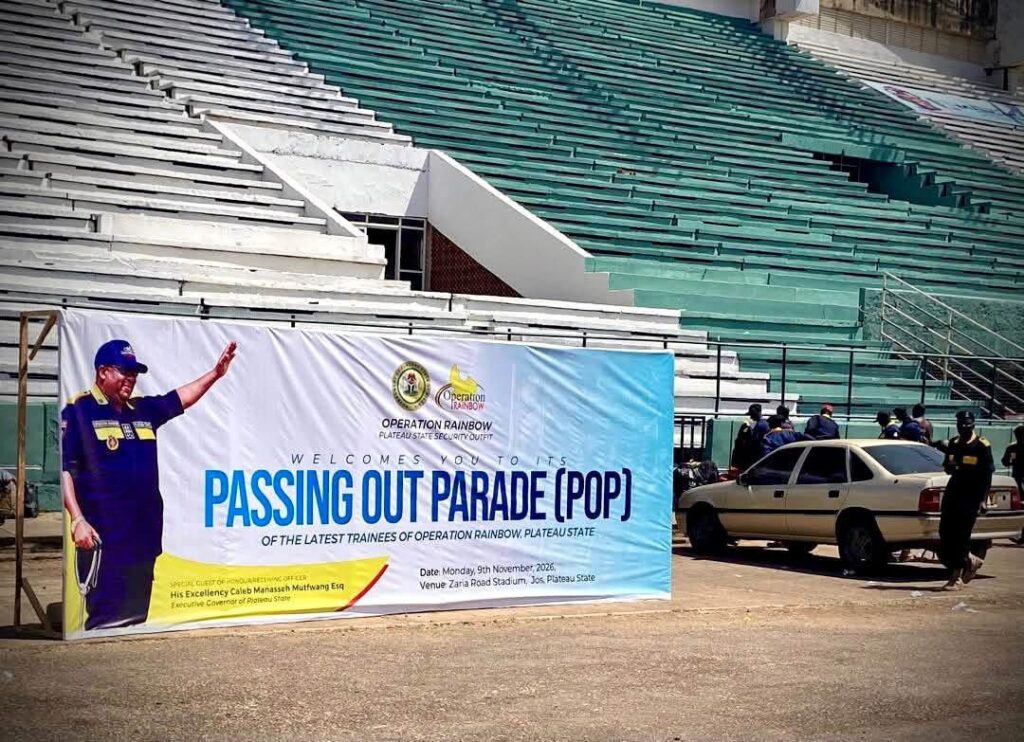
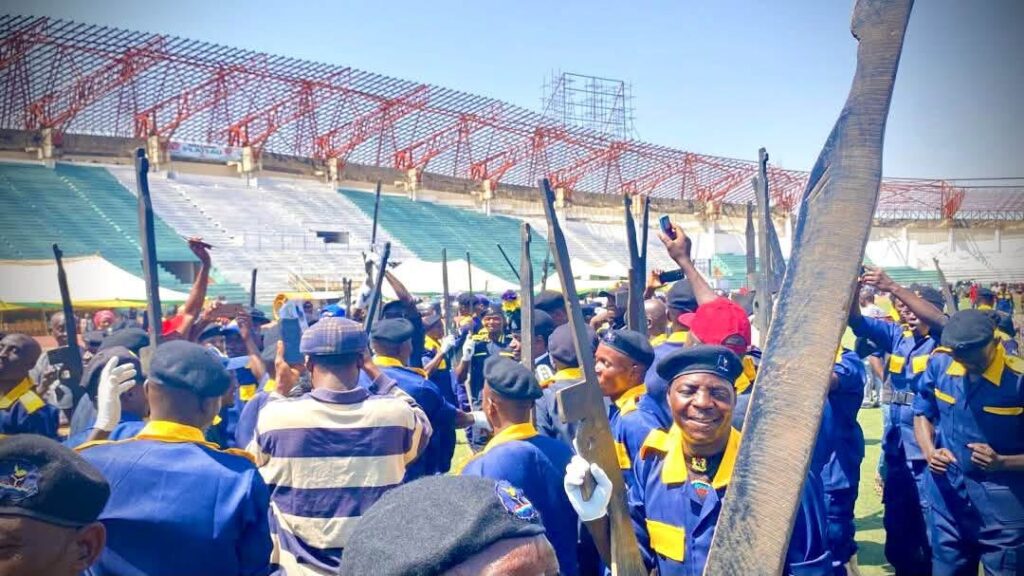
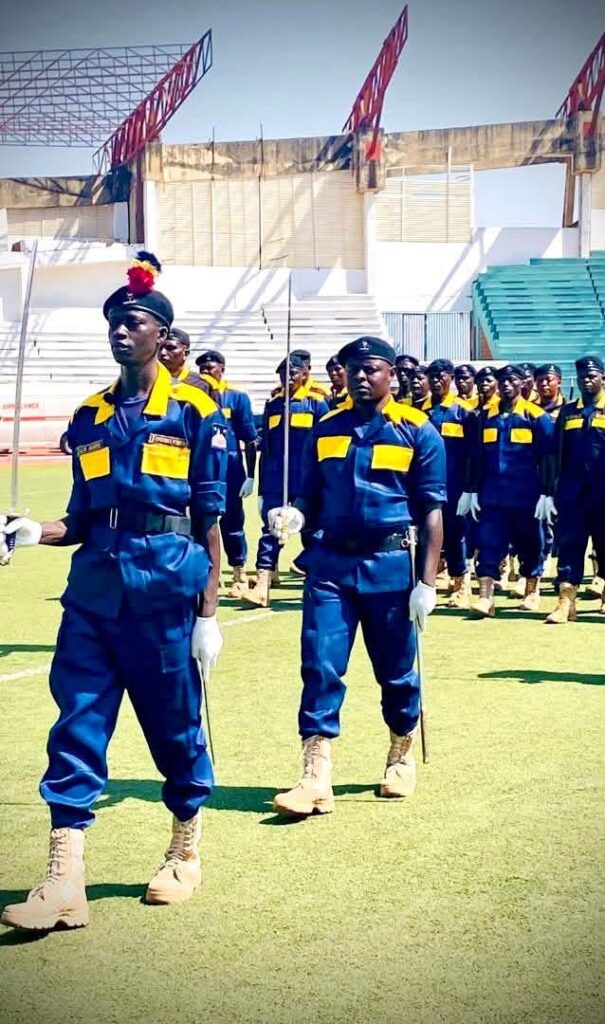
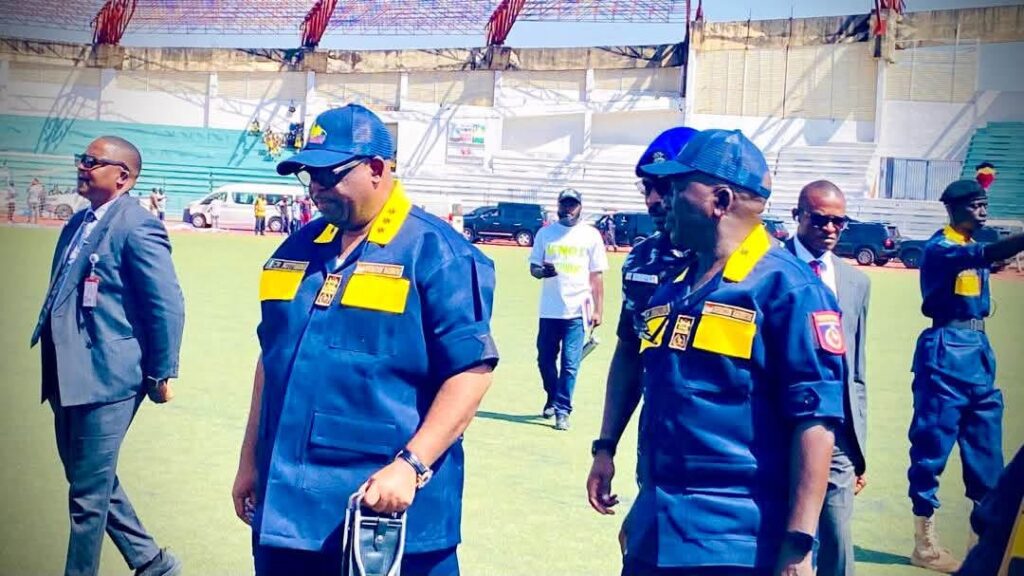
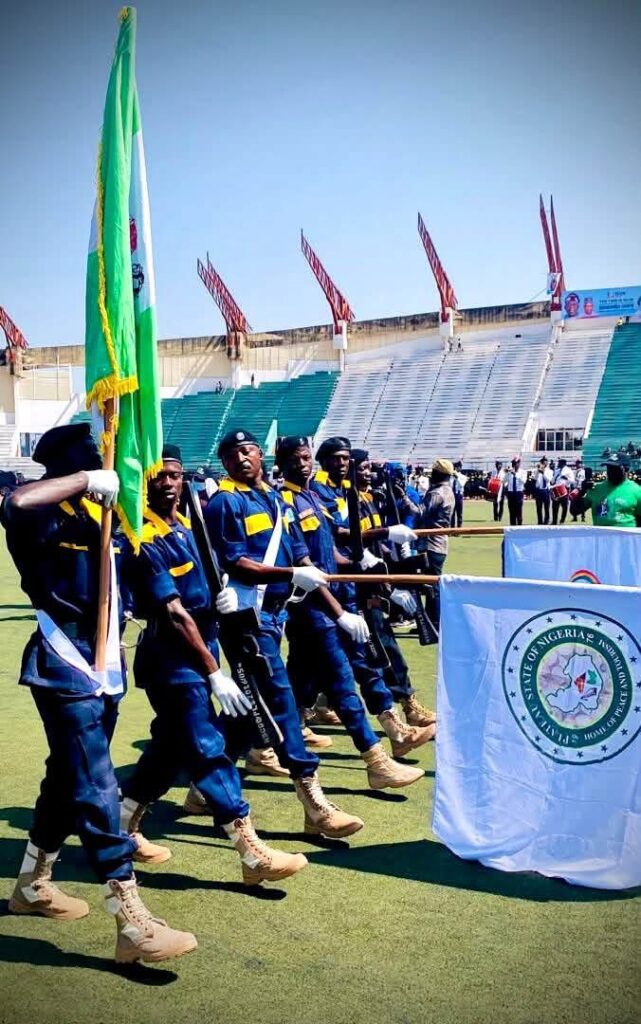
The operatives successfully completed their training and passed out on Monday, November 9, 2026, during a colourful parade held at the New Zaria Road Stadium in Jos.
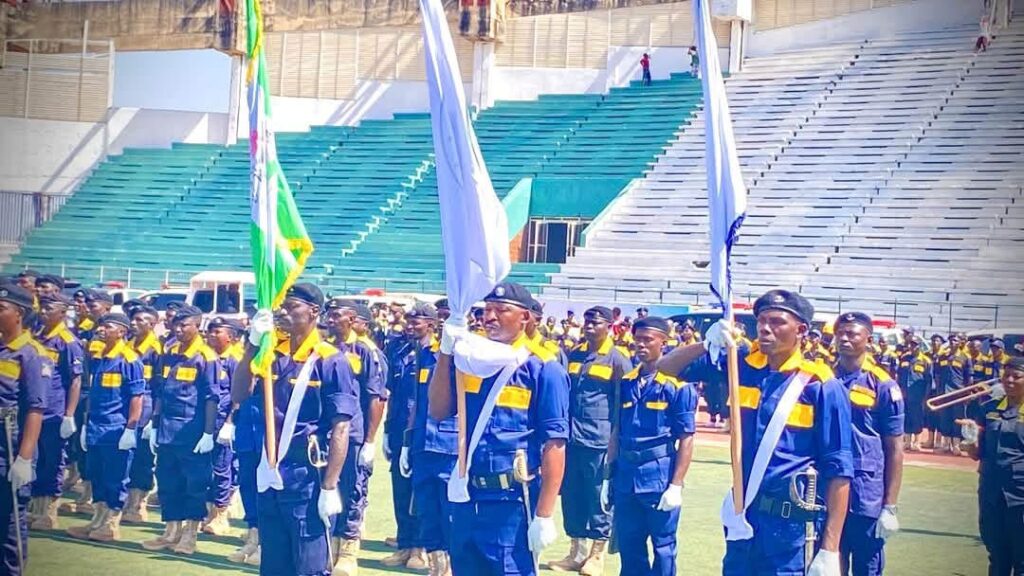
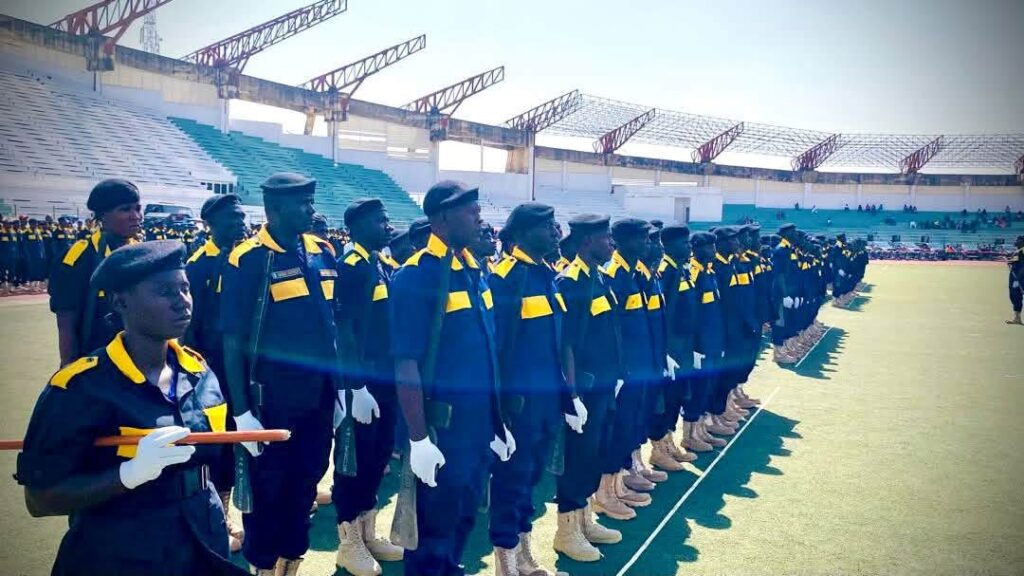
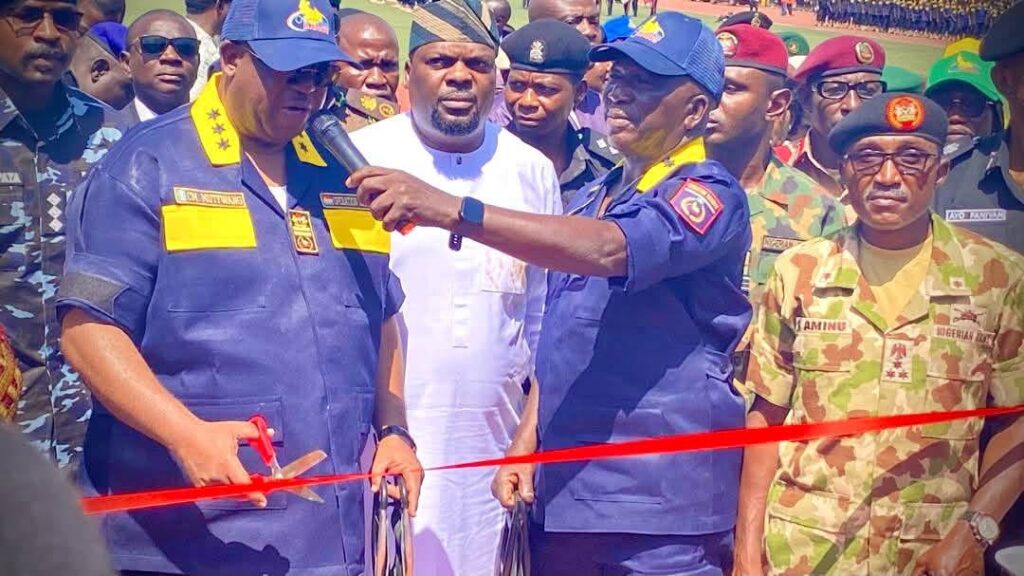
The retraining programme is aimed at strengthening the capacity of the operatives in intelligence gathering, early warning mechanisms, community engagement and rapid response to security threats.
The initiative is also expected to improve collaboration between local security structures and other conventional security agencies, particularly in identifying potential threats and preventing security breaches before they escalate.
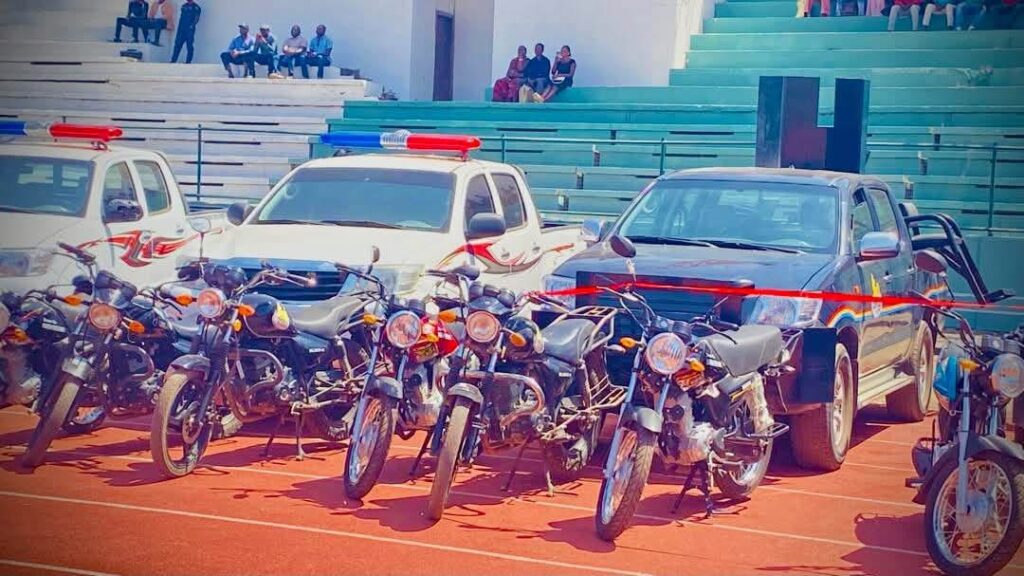
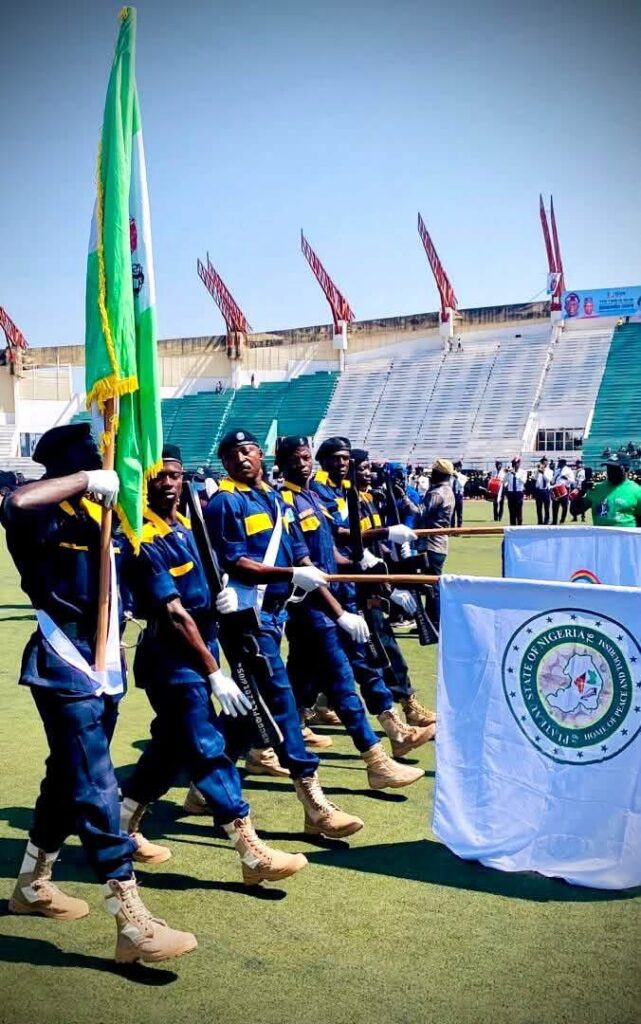
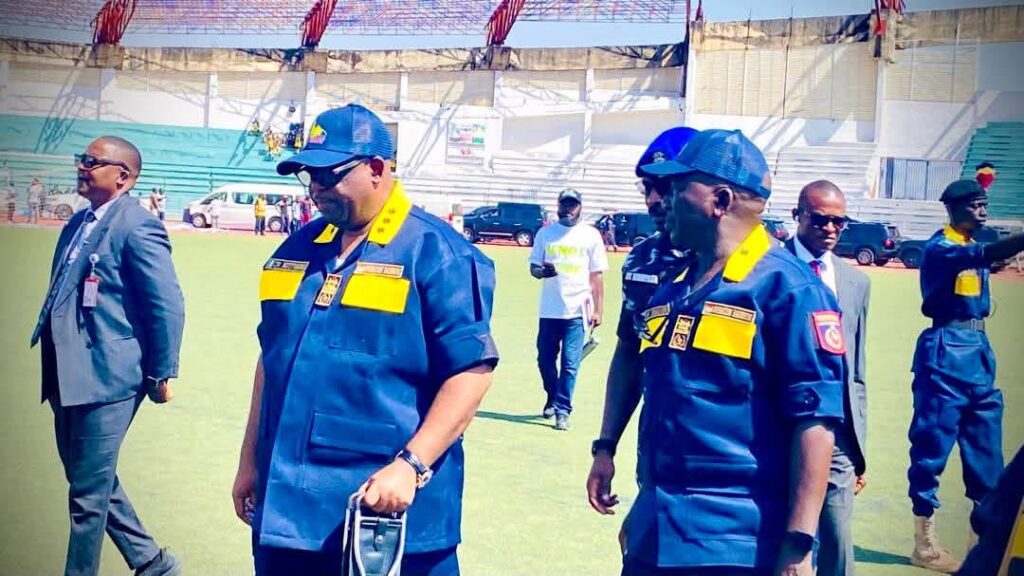
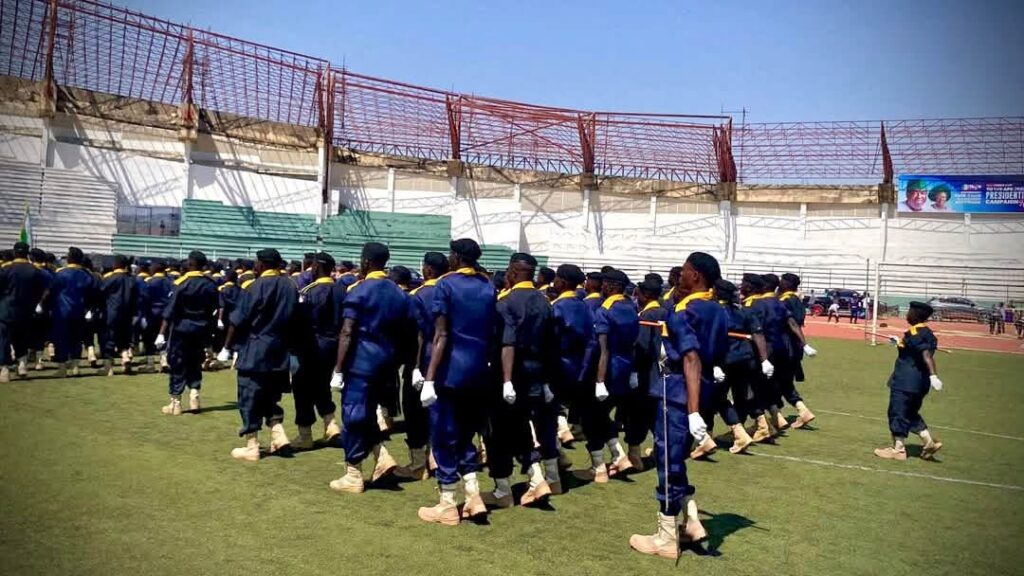
The provision of operational vehicles is another significant step towards improving the mobility, operational efficiency and response capabilities of Operation Rainbow personnel, especially in communities where timely security intervention is critical.
With the retraining of the 353 operatives and the additional logistical support, the state government is reinforcing its commitment to community-driven security and proactive measures to protect lives and property.
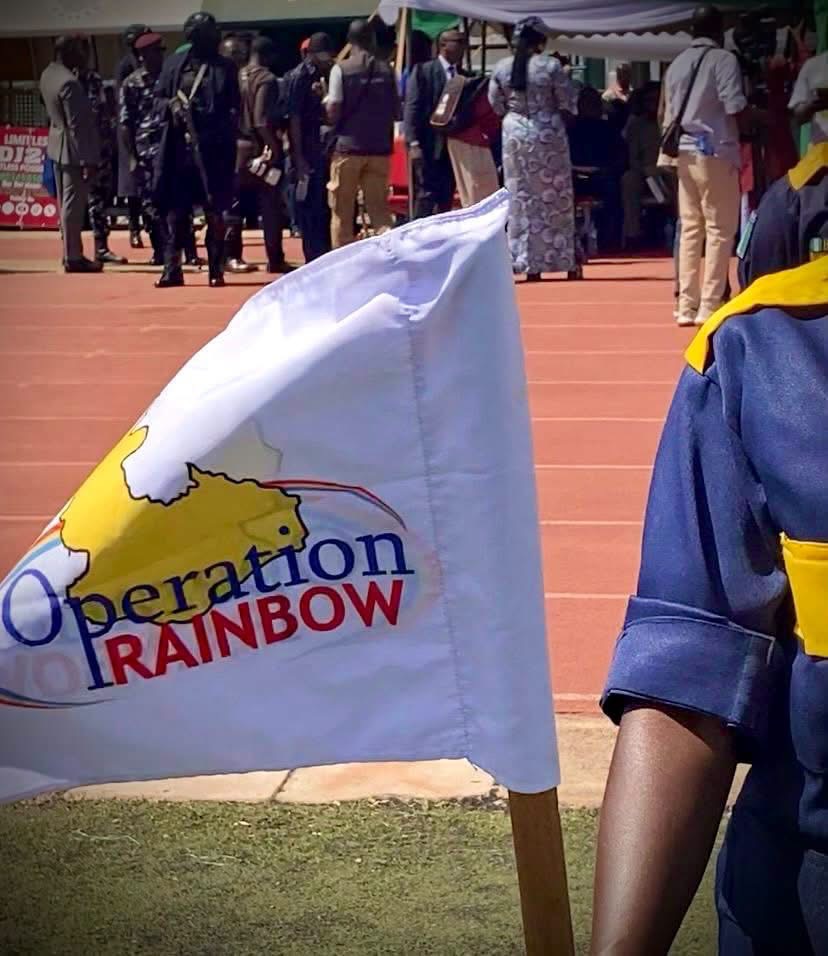
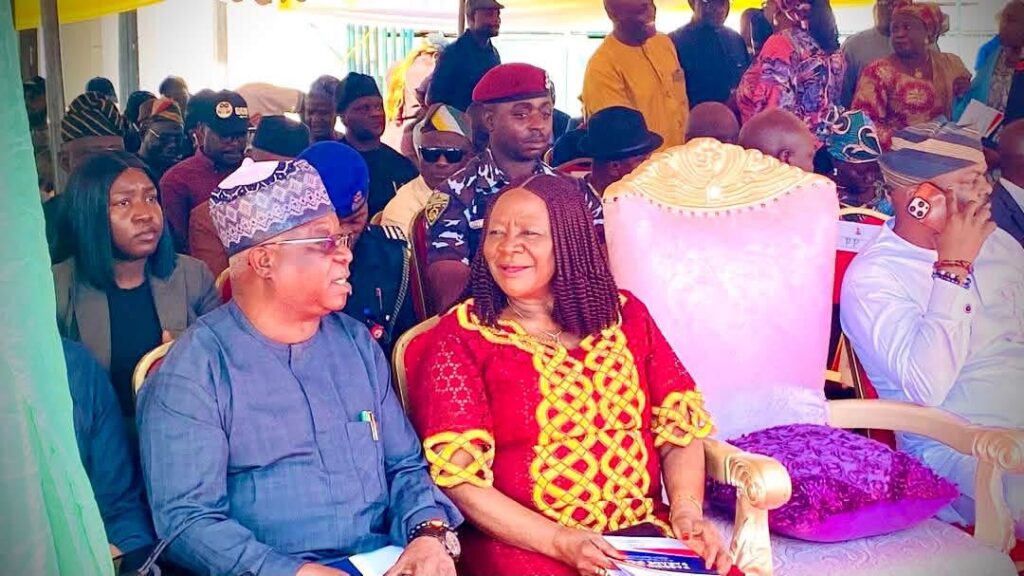
Operation Rainbow remains an important component of Plateau State’s local security framework, particularly in strengthening grassroots intelligence and fostering cooperation between security personnel and local communities.
The development represents another step in the state’s ongoing efforts to build a more responsive, coordinated and effective security system across Plateau State.
The Inter-Party Advisory Council, IPAC, in Cross River State has welcomed the directive by Governor Bassey Otu for the arrest of suspected thugs accused of attacking opposition figures, describing it as a step towards protecting political participation and preventing violence ahead of the 2027 elections.
The council said the action would help protect the rights of political parties and create an atmosphere for peaceful political competition in the state.
The state chairman of IPAC, Engr. Effiom Edet Okon, stated this in a press statement issued on Monday, November 9, while outlining the council's plans to promote political accountability and peaceful coexistence ahead of the elections.
The council, however, urged political parties, candidates and their supporters to embrace issue-based campaigns, responsible communication and peaceful competition, warning that political ambition should not endanger lives or public order.
As part of its accountability drive, IPAC announced plans to tour the 18 local government areas to inspect government projects, assess their level of implementation and determine their impact on communities.
It said the exercise would also identify areas requiring intervention and provide recommendations for improved service delivery.
The council disclosed that the tour would involve local government chairmen, security agencies, the Independent National Electoral Commission, INEC, political party leaders, aspirants, candidates and community representatives.
IPAC also announced plans to organise a statewide political stakeholders' conference to promote dialogue, consensus-building and responsible political participation.
In addition, it scheduled a political parties' peace walk for Saturday, December 5, 2026. The event has as its theme, 'Unity in Diversity, Peace for a Greater Cross River'.
The council reaffirmed its commitment to protecting the democratic space and ensuring that political disagreements do not degenerate into violence as preparations for the 2027 general elections gather momentum.
IPAC welcomes directive for arrest of suspected thugs attacking opposition figures
-

 News6 hours ago
Troops Arrest Suspected Gunrunner, Neutralise Two Terrorists in Plateau
-
Business4 days ago
FG Backs Risk-Based Capital, Urges Insurance Directors to Move Beyond Passive Compliance
-
News1 day ago
Makinde Visits COCIN Headquarters in Jos, Urges Christians to Shape Nigeria’s Political Future
-
News4 days ago
The New York Times reportedly in talks to buy Letterboxd for $330 million