News
How much personal data should you really give an app? – Technology Times

There was a time when giving out personal information meant writing your name and phone number on a form, handing over a photocopy of an identity card or filling in an address on a paper document.
That world is disappearing. Today, Nigerians routinely enter personal information into banking apps, shopping platforms, ride-hailing services, social networks, entertainment platforms and government websites. Sometimes it happens several times a day, often without much thought.
A banking app may ask for identity details. A ride-hailing app wants your location. An online store needs your address. A social platform may ask for access to your photographs, microphone or contacts. And then there are the less obvious requests.

That world is disappearing. Today, Nigerians routinely enter personal information into banking apps, shopping platforms, ride-hailing services, social networks, entertainment platforms and government websites. Sometimes it happens several times a day, often without much thought.
An app wants access to your entire contact list. Another wants continuous access to your location. Yet another asks for an identity number that appears to have little connection with what you are trying to do. At some point, a reasonable question arises: how much information is too much?
Nigeria’s data protection framework offers a surprisingly straightforward starting point.
The answer is not “whatever the app asks for”. The Nigeria Data Protection Commission (NDPC) says personal data should be processed fairly, lawfully and transparently. It should be collected for specified and legitimate purposes and should be “adequate, relevant, and limited to the minimum necessary” for the purpose for which it is being processed.
That last part is important. It is known as data minimisation, and it essentially means that because an organisation can collect a particular piece of information does not mean that it should.
For ordinary users, the principle offers a useful question whenever a digital service asks for information: why does it need this?
If the answer is clear and connected to the service, the request may make sense. If the explanation is vague, users may want to pause before clicking “allow”.
Personal data: Every app has a reason for collecting our information
There is no universal list of information that every digital service should be allowed to collect. The answer depends on what the service actually does.
A bank needs information that allows it to identify customers, comply with financial regulations and provide banking services. A ride-hailing platform needs a user’s location to match passengers with drivers. A delivery company needs an address if it is going to deliver something to your doorstep. Those are relatively easy to understand.
The questions become more interesting when an application begins asking for information that does not appear essential to the service.
Why does a calculator need access to your contacts?
Why does a simple application need continuous access to your location?
Why does a service unrelated to photography need access to your entire photo library?
There may sometimes be legitimate technical explanations. But the point of data minimisation is precisely that organisations should be able to connect the information they collect to a legitimate purpose.
The NDPC’s own privacy policy reflects this broader approach. Personal information should be collected for specified, explicit and legitimate purposes, retained only for as long as necessary and protected against unauthorised or unlawful processing, loss, destruction or damage.
In other words, clicking “I agree” does not turn privacy into a free-for-all.

The questions become more interesting when an application begins asking for information that does not appear essential to the service. Why does a calculator need access to your contacts? Why does a simple application need continuous access to your location? Why does a service unrelated to photography need access to your entire photo library? There may sometimes be legitimate technical explanations. But the point of data minimisation is precisely that organisations should be able to connect the information they collect to a legitimate purpose.
Your NIN deserves a different level of caution
The issue becomes more serious when the information being requested is a powerful identifier such as the National Identification Number.
The National Identity Management Commission (NIMC) has warned Nigerians against indiscriminate disclosure of their NIN.
Its advice is direct: “The NIN should be closely guarded by individuals and not revealed to all and sundry except to relevant authorities when requested.” That warning matters in an economy increasingly built around digital identity.
A NIN is not simply another phone number or email address. It can serve as an important identifier linking an individual to different services and records. This means Nigerians may need to become more selective about who receives it and why.
The same thinking applies to other sensitive information, including bank verification details, biometric information, passport details and financial records.
The convenience of completing an online registration should not automatically outweigh the consequences of unnecessarily distributing information that can be difficult to replace once exposed.
The problem with data is that it can travel
When personal information is given to an organisation, most users assume it will stay within the organisation’s systems and be used for the purpose they had in mind. That is not always how the digital world works.
Information can move between systems. It can be shared with service providers. It can remain in databases for years. It can be exposed through cyberattacks or compromised through poor security practices.
In 2024, digital rights organisation Paradigm Initiative raised concerns after reporting the discovery of websites allegedly offering sensitive personal and financial information belonging to Nigerians for as little as ₦100.
The reported information included NIN, BVN, virtual NIN, driving licence, international passport, Tax Identification Number, Permanent Voter’s Card and telephone numbers.
Paradigm Initiative called for stronger measures to protect Nigerians’ personal information. The episode illustrates an uncomfortable reality of the digital economy: once information has been collected, the individual no longer has complete control over where it sits or who might eventually gain access to it.
That is why the question of privacy does not end with the user. It also belongs to the organisation holding the data.

When personal information is given to an organisation, most users assume it will stay within the organisation’s systems and be used for the purpose they had in mind. That is not always how the digital world works. Information can move between systems. It can be shared with service providers. It can remain in databases for years. It can be exposed through cyberattacks or compromised through poor security practices. In 2024, digital rights organisation Paradigm Initiative raised concerns after reporting the discovery of websites allegedly offering sensitive personal and financial information belonging to Nigerians for as little as ₦100.
Privacy is not simply about secrecy
It is easy to think of data privacy as something that matters only to people who have something to hide. That is too narrow a view. Privacy is also about control.
Who knows your identity? Who knows where you live? Who knows where you travel? Who has your financial information? Who can connect several apparently unrelated pieces of information and build a detailed picture of your life?
The more information an organisation holds, the greater the potential consequences if that information is misused, exposed or retained unnecessarily.
For some categories of information, there is another problem: you cannot simply change them.
A password can be replaced. A compromised NIN is a different proposition. So is exposed biometric information.
This is one reason why data minimisation matters beyond regulatory compliance. It can also be understood as a basic form of digital risk management.
Nigerian law gives consumers more control
Nigeria’s data protection framework is anchored by the Nigeria Data Protection Act 2023, which established the NDPC as the country’s independent data protection regulator.
The framework provides data subjects with a number of rights concerning their personal information.
These include the right to know how their data is being processed, to access personal information, to request correction of inaccurate information and, in applicable circumstances, to request erasure.
There are also provisions dealing with matters such as objection to certain processing, data portability and automated decision-making.
This is worth remembering because privacy policies can sometimes feel like contracts written for someone else.
They are often long. The language can be technical. And the temptation is to scroll to the bottom and click “accept”. But accepting a privacy policy does not mean that an organisation is suddenly exempt from its obligations under Nigeria’s data protection framework.
Companies and public institutions still have responsibilities concerning how personal information is collected, processed, stored and shared.
The five-second pause
There is a simple habit that could make digital life slightly safer. Before giving an app access to something personal, pause for a few seconds. Ask what it needs the information for.
If a service asks for your location, is the location necessary for the service?
If it wants access to your contacts, does the feature genuinely require them?
If it requests your NIN, is there a legitimate reason for the organisation to have it?
If you refuse, does the service still work?
And, perhaps most importantly, what happens to the information after you have handed it over?
These questions do not require technical expertise. They are simply the digital equivalent of asking someone why they need a copy of your identity document before handing it over.
The responsibility cannot rest entirely with users
There is a danger in making privacy sound like another problem that ordinary Nigerians must solve for themselves. The person downloading an app is only one part of the equation. Organisations that collect personal information have responsibilities too.
The NDPC’s data protection principles cover purpose limitation, data minimisation, accuracy, storage limitation and security, among other requirements. The framework can also apply in specified circumstances to organisations outside Nigeria that process the personal data of people in Nigeria.
That is significant because Nigerians increasingly interact with digital companies headquartered elsewhere. A person in Lagos may bank through a local institution, shop through an international platform, communicate through a global social network and store files on an overseas cloud service, all within the same day.
Data does not respect national borders simply because the person generating it lives in Nigeria.
Digital transformation needs trust
Nigeria’s digital economy cannot function without data. Banks need customer information. Healthcare platforms need patient records. E-commerce companies need delivery details. Telecommunications operators need subscriber information. Government services increasingly depend on digital identity.
The objective, therefore, cannot realistically be to stop collecting personal information. The more useful question is whether the information being collected is necessary, proportionate, properly protected and used for the purpose for which it was obtained.
That is where the principle of data minimisation becomes particularly relevant. Personal information should be “adequate, relevant, and limited to the minimum necessary” for the purpose for which it is processed.
It is a relatively simple idea for an increasingly complicated digital economy. NIMC’s caution about protecting the NIN reinforces it from the identity-management perspective. Concerns raised by Paradigm Initiative about exposed Nigerian data demonstrate the consequences that can follow when sensitive information ends up in the wrong hands.
For consumers, the lesson is equally straightforward. The next time an app asks for access to something personal, there is no harm in pausing before clicking “allow”.
The question is not whether the app wants your data. It probably does. The better question is whether it genuinely needs it.


Former presidential aide Laolu Akande has criticised the African Democratic Congress, ADC, presidential candidate Atiku Abubakar's reported position on power returning to the North, describing the argument as an insult to Nigerians from the region.
Akande, a former Senior Special Assistant to the President on Media and Publicity in the Office of the Vice President, made the remarks while speaking on Symfoni TV on Friday.
Speaking on the readiness and viability of presidential candidates ahead of the coming election, Akande argued that the country must maintain the principle of rotational presidency to promote a sense of belonging among its various regions.
“Atiku is just basically saying that, okay, the North is angry; we want power back. And that idea, with due respect to our brothers in the North, is an insult. It’s an insult. This country, we must maintain rotational presidency for purposes of building a sense of belonging,” he said.
Speaking on the ADC's choice of presidential candidate, he said, “If they were serious, they should have picked Amaechi, or they should have prevented Obi from leaving, and then Atiku would have been a star.”
‘Atiku’s push for return of power to North is insult’ — Laolu Akande
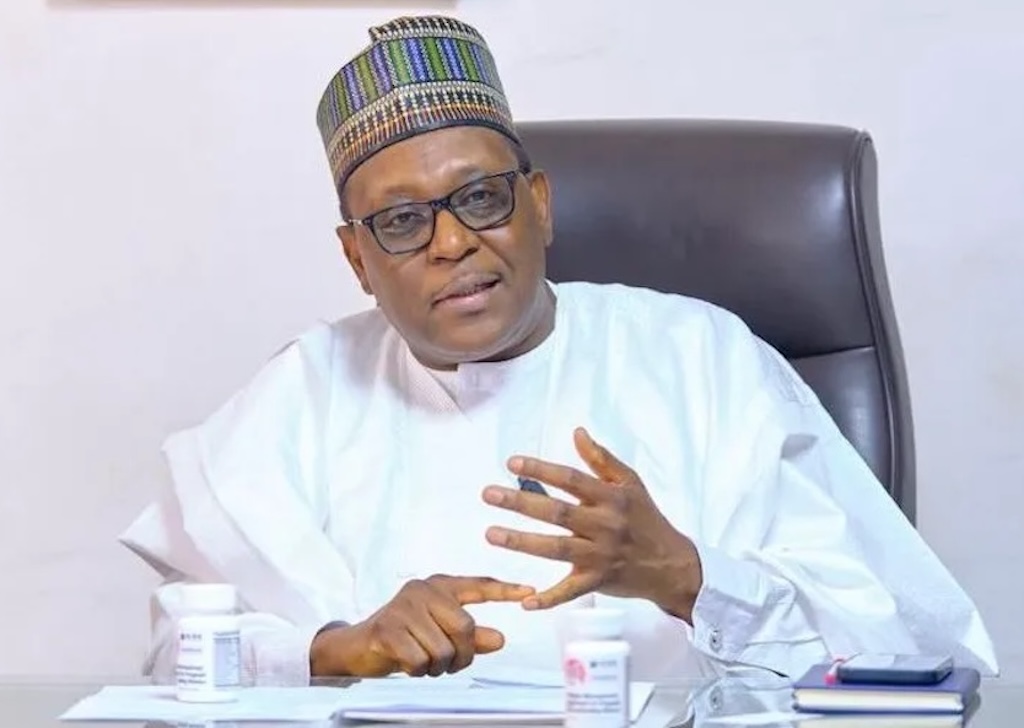
The Coordinating Minister of Health and Social Welfare, Muhammad Pate, has confirmed that the Ebola virus detected in Nigeria is highly similar to the virus identified in Kenya’s first imported case.
Mr Pate disclosed this on Friday during a briefing at the Federal Ministry of Health in Abuja, saying genomic sequencing showed that the viruses differed by only one mutation.
He said the analysis was conducted by sequencing teams at the Nigeria Centre for Disease Control and Prevention (NCDC) and the Institute of Genomics and Global Health at Redeemer’s University, Ede, Osun State, with the team led by virologist Christian Happi.
However, he cautioned that the finding does not establish how the Nigerian first case acquired the infection.
“Based on the genomic analysis, there is no evidence of travel of that index case in Kenya that links it to Nigeria, but the viruses are appearing to be related,” he said.
He added that the finding could change the understanding of the route of transmission as further investigations and testing continue.

Kenya has so far recorded nine confirmed Ebola cases caused by Bundibugyo virus, including one death, according to the European Centre for Disease Prevention and Control (ECDC). Eight of the cases were linked to the country’s first imported case from the Democratic Republic of the Congo (DRC), including four healthcare workers.
Africa CDC probes link
The genomic finding came on the same day the Africa Centres for Disease Control and Prevention (Africa CDC) said it is investigating a possible connection between Nigeria’s case and Kenya’s first imported case.
The agency said both patients had travelled through Entebbe International Airport in Uganda on 3 October, prompting investigations into whether they had shared equipment or had other contact. Africa CDC, however, stressed that no connection had been established between the infections.
The Kenyan patient travelled from the DRC through Uganda before arriving in Nairobi. He later died, becoming the first recorded Ebola death in Kenya’s current outbreak.
The Nigerian patient also passed through Uganda, but Ugandan authorities had earlier rejected suggestions that this established the country as the source of her infection.
Uganda denies active case
On 21 October, Uganda’s Ministry of Health said it had no confirmed active Ebola case and that the Nigerian patient’s transit through the country did not establish that she contracted the virus there.
The ministry said preliminary information indicated that the Nigerian woman had travelled to eastern DRC for business and passed through Uganda in early October without showing symptoms. It said the location of her exposure remained under investigation.
The new genomic finding now provides evidence of similarity between the Nigerian and Kenyan infections, although Nigerian authorities have not established that the patient was infected in Kenya.
One confirmed case
Mr Pate said Nigeria still has only one confirmed Ebola case and that authorities were continuing contact tracing, quarantine and additional testing of contacts.
Some tests have returned negative results, while others are pending, he said.
He urged Nigerians to remain vigilant but calm, saying there is no need for panic.
“We will continue to work diligently to ensure that we contain this virus as much as possible, and that we avoid a situation that spills over to the communities,” he said.
READ ALSO: Ebola: Atiku demands details of FG’s N10bn emergency fund
The minister said the government is also strengthening infection prevention and control measures in health facilities and would train health workers on how to identify and manage suspected cases.
He urged hospitals to notify public health authorities of suspected cases and encouraged Nigerians to observe basic preventive measures, including regular handwashing and hygiene.
Mr Pate also said Ebola is not currently known to be transmitted through the air but through close contact with infected body fluids.
He urged Nigerians to rely on information from public health authorities, including the NCDC, Federal Ministry of Health, World Health Organisation and Africa CDC, rather than unverified information on social media.
Discover more from Premium Times Nigeria
Subscribe to get the latest posts sent to your email.
-

 News17 hours ago
Obi, Kwankwaso to hold Middle Belt Youth, Village Hall Meeting in Jos
-
News4 days ago
Mamdani says feds have abdicated on AI, urges New Yorkers to push back
-
News3 days ago
Meta’s Muse hits 10M U.S. downloads in 40 days, a milestone reached by only 11 other apps
-
Business3 days ago
How Your Side Hustle Income Ends Up in Your RSA