News
Expert backs suicide decriminalisation

Taiwo Obindo, a psychiatrist, says decriminalising attempted suicide will enable more people to access mental health assessment, treatment and psychosocial support, while reducing barriers to seeking professional help.
Mr Obindo, professor of psychiatry and honorary consultant at the University of Jos and Jos University Teaching Hospital, said this on Tuesday. He explained that not all suicide attempts were linked to mental health conditions, emphasising that each case should be carefully assessed to determine underlying causes and appropriate interventions.
“Let me start by saying that not all cases of suicide or attempted suicide are mental health cases,” he said.
According to him, about 80 to 90 per cent of people who died by suicide were likely to have underlying depression, while other mental health conditions could contribute.
The psychiatrist said impulsive individuals might make decisions before adequately thinking through consequences, making professional assessment necessary to identify possible underlying mental illness and determine appropriate support needs.
“Those who do not have mental health conditions are then given psychosocial support to help them move on with life,” he said.
Mr Obindo, also chairman of the West Africa College of Physicians (Nigeria chapter), said warning signs included withdrawal, hopelessness, persistent low mood and loss of interest in activities.
He said poverty, significant losses, impulsivity, anxiety disorders, schizophrenia and chronic illnesses could also contribute to suicidal thoughts, increasing the need for timely mental health interventions.
The immediate past president of the Association of Psychiatrists in Nigeria said postpartum mental health conditions could predispose affected individuals to suicide or infanticide if untreated.
He said the federal government’s move to decriminalise attempted suicide, following Federal Executive Council approval, would allow the matter to proceed to the National Assembly.
Mr Obindo said rather than criminalising people who attempted suicide, they should be assessed and provided with appropriate treatment, rehabilitation services or psychosocial support based on identified needs.
He also called for the implementation of the National Mental Health Act and the establishment of a dedicated mental health department within the Federal Ministry of Health.
(NAN)




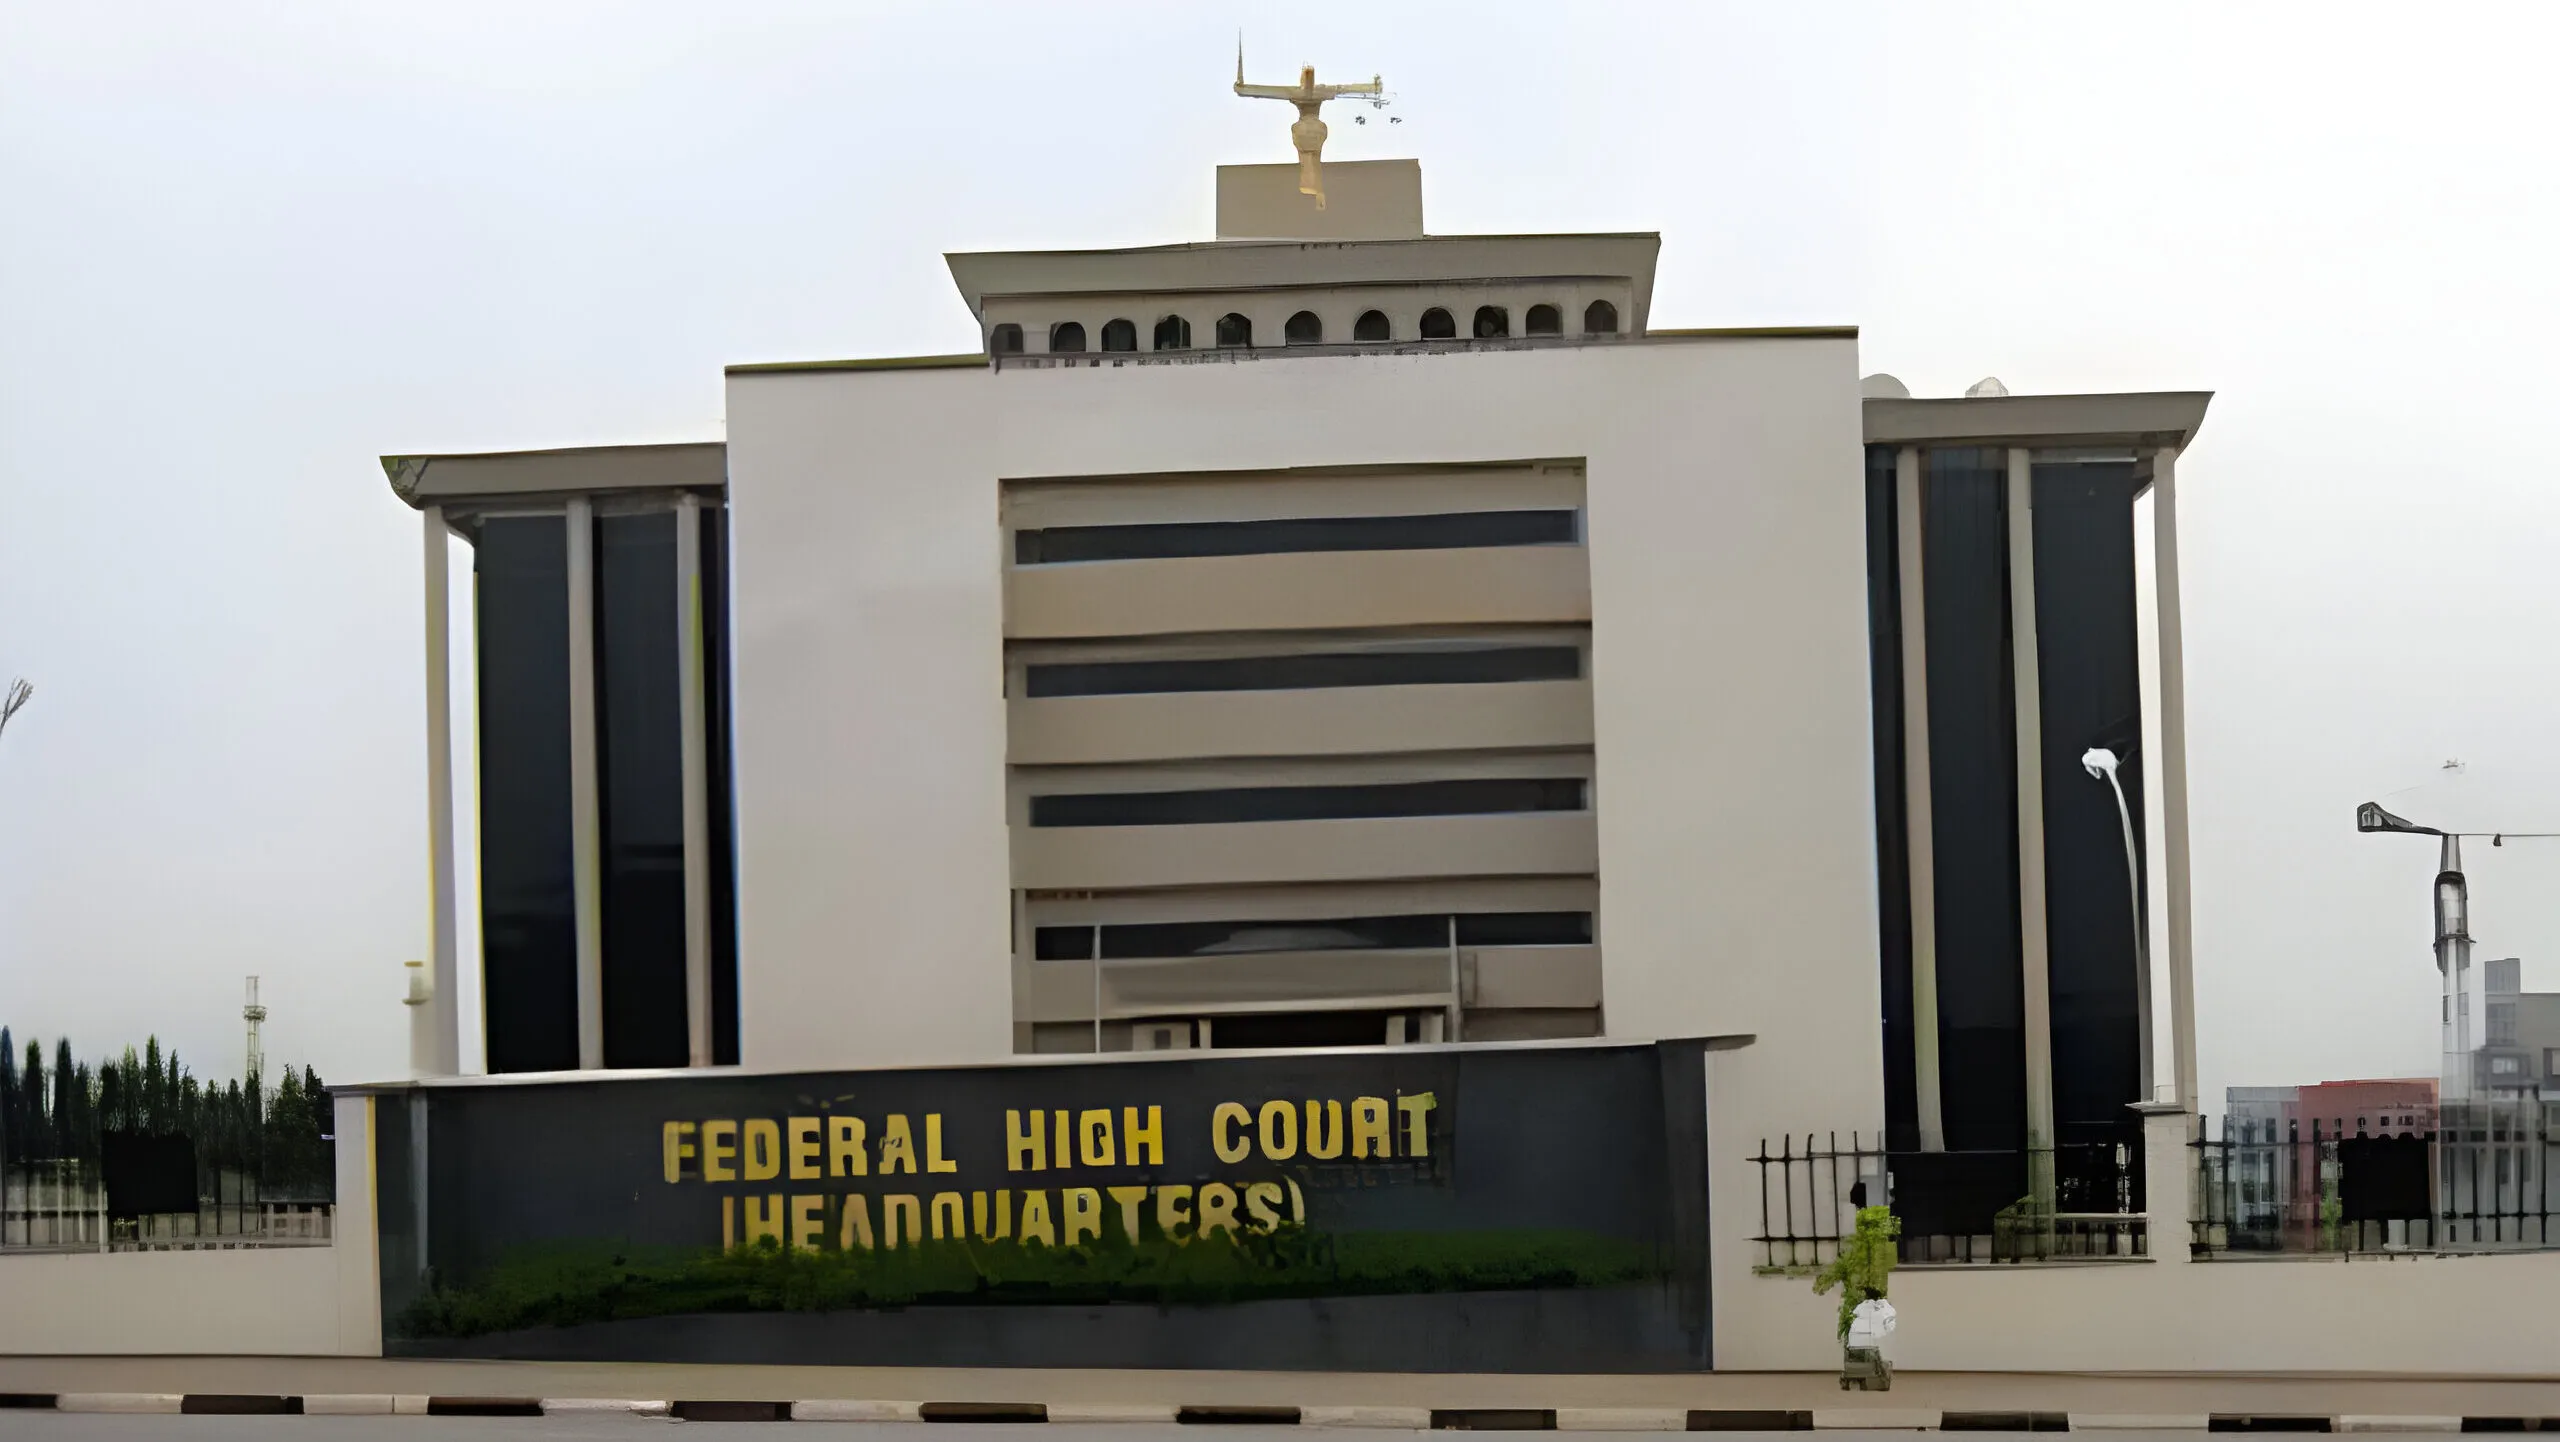
The Federal High Court in Abuja on Tuesday fixed Nov. 24 for hearing in a suit filed by the Chartered Institute of Forensics and Certified Fraud Investigators of Nigeria (CIFCFIN) against the Institute of Chartered Accountants of Nigeria (ICAN).
CIFCFIN is challenging the power of ICAN to train and issue qualifying certificates to forensic professionals.
The matter, which is before Justice Joyce Abdulmalik, was initially scheduled for mention on Tuesday but the case was adjourned to enable parties appear properly before the court.
The News Agency of Nigeria (NAN) reports that CIFCFIN, through its counsel, Shaibu Aruwa, a Senior Advocate of Nigeria (SAN), sued ICAN as the sole defendant in the suit marked FHC/ABJ/CS/1559/2026.
CIFCFIN argued that ICAN cannot offer a “Certification Programme culminating in the award of Certified Forensic Accountant of Nigeria (CFAN).”
It submitted that this was in line with the combined interpretation of Sections 2(a) – (i),3(1)(a) and 4(a) – (c), 6(2), 12(2), 13, (1) () and (g), 17(1l) (a) and (b) and 22 of the Chartered Institute of Forensics and Certified Fraud Investigators of Nigeria (Establishment) Act No. 45, 2022,

Mohammed Arafat, the Head of Legal and Corporate Services of CIFCFIN, maintained in a supporting affidavit that ICAN’s invitation to applicants for a seven-day professional certification programme culminating in the award of Certified Forensic Accountant of Nigeria (CFAN), is outside its mandate and could confuse the general public.
The plaintiff alleged that ICAN had invited applicants in the fields of knowledge of chartered accountants, compliance managers, bankers, investment analysts, auditors, and anti-corruption agencies staff and other institutions to register for the programme.
CIFCFIN, therefore, prayed the court for an order setting aside and nullifying the award of the qualification or the CFAN certificate, or any other qualification or certificate in the field and practice of forensics in Nigeria by ICAN.
It urged the court to make an order for the defendant to withdraw, retract or cease any publication, gazette notice, or public representation asserting that it has power to certify or license.
CIFCFIN also sought an order of perpetual injunction restraining ICAN, its council, etc, from issuing, advertising or recognising CFAN qualification, designation, licence or certification or any title or award identical or similar to those created under the provisions of its Act.
It further sought a declaration that “by the combined provisions of Sections 2(a) -(i), 3(1)(a) and 4(a)- (c), 6(2), 12(2), 13, (1)(0) and (g), 17(1)(a) and (b) and 22 of the Chartered Institute of Forensics and Certified Fraud Investigators of Nigeria (Establishment) Act No. 45. 2022, the defendant cannot offer ‘Certification Programme’ culminating in the award of CFAN.”
(NAN)
Discover more from Premium Times Nigeria
Subscribe to get the latest posts sent to your email.
-

 Business2 days ago
Lingzhi Global, NACOFTAN Announce 2026 Coffee Festival in Cross River
-
Events2 days ago
Peace Walk: WOPPI Urges Plateau Citizens to Invest in Peace Every Day
-
News2 days ago
INEC declares APM’s Adamu Yakubu winner of Sakwa bye-election in Bauchi
-
 Health2 days ago
Nigerian hospitals collaborate to perform tele-robotic surgery