News
Lotus Bank flags dta privacy risks from unapproved workplace AI tools – Technology Times

Lotus Bank has warned employees against entering confidential, personal or customer information into unapproved artificial intelligence (AI) tools, cautioning that the growing workplace adoption of the technology could expose sensitive data to privacy and cybersecurity risks.
The warning was delivered Wednesday during the Lotus Bank 2026 Cybersecurity and Data Privacy Awareness Webinar, where participants were advised to use approved AI platforms for organisational work, verify AI-generated outputs and maintain human oversight over consequential decisions.
“Do not enter confidential, personal or client information into unapproved AI services,” the webinar presentation stated. The guidance highlights the need for organisations to balance the productivity benefits of AI with safeguards for customer information, business records and other sensitive data.
AI tools can help employees draft documents, analyse information, generate code and automate routine tasks. However, submitting confidential material to services that have not been approved by an organisation can create risks involving data handling, retention, access and potential disclosure.

AI tools can help employees draft documents, analyse information, generate code and automate routine tasks. However, submitting confidential material to services that have not been approved by an organisation can create risks involving data handling, retention, access and potential disclosure.
Lotus Bank: AI creates new cybersecurity challenges
Beyond the risks associated with employees’ use of AI tools, the webinar identified the technology as one that cybercriminals could exploit to strengthen their attacks.
According to the presentation, attackers may use AI to generate convincing phishing messages, impersonate individuals through synthetic media, produce misleading content and create insecure code. These capabilities can make it more difficult for employees and customers to distinguish legitimate communications from fraudulent requests.
The presentation warned that modern phishing attacks could involve personalised messages, convincing branding, impersonation of executives, colleagues or suppliers, fake login pages, malicious attachments, and fraudulent requests delivered through voice calls and messaging applications.
It also cautioned against relying on spelling and grammatical mistakes alone to identify phishing attempts, noting that fraudulent messages can appear professional and convincing.
Lotus Bank employees were advised to examine senders’ identities, consider whether they were expecting a communication, inspect links before opening them and verify unusual requests through established, independent channels.
The presentation placed particular emphasis on checking requests involving login credentials, verification codes, confidential information or payments before taking action.
“Trust should never replace verification when money, access or sensitive information is involved,” the presentation stated.
The advice underscores the importance of combining technical security controls with employee awareness, particularly when attackers exploit trust and urgency to persuade victims to bypass established procedures.
Employees urged to safeguard customer information
The webinar also stressed that having access to information does not automatically give employees permission to disclose, copy or transfer it.
Participants were advised to share sensitive information only with authorised recipients, verify recipients before sending files, and use approved storage and transfer platforms.
The presentation further recommended restricting access appropriately, complying with information-retention requirements and securely disposing of records when they are no longer needed.
Employees were cautioned against using personal accounts or unapproved tools to handle business information and urged to report misdirected communications and suspected data exposure promptly.
The guidance covers customer and employee personal information, financial and payment details, business plans, contracts, intellectual property, security configurations and confidential operational records.
These safeguards are particularly relevant to financial institutions, where employees routinely handle sensitive customer information and exchange documents with customers, suppliers and other external parties.
During the question-and-answer session, a participant raised concerns about relationship managers and other employees who receive files from customers and business partners, noting that malicious attachments could infect devices and potentially expose organisational information.
In response, Sodiq Bello, the bank’s chief information security officer, said the institution had measures in place to protect files and information received from customers and other external parties.
Bello also advised employees who handle such information on personal devices to activate available security features and consider endpoint protection, including antivirus software.
He urged staff to exercise caution before accepting, downloading or installing files received from others.
Employees, he explained, should verify senders’ identities and establish whether a communication or file-sharing request is consistent with their previous interactions.
Bank stresses responsible AI use and access controls
The webinar’s recommendations extended beyond AI applications to broader cybersecurity practices, including identity protection, access management and the remediation of technical vulnerabilities.
Employees were advised to use strong, unique passwords, enable multi-factor authentication where available or required, reject unexpected authentication prompts, and avoid sharing passwords or one-time verification codes.
Organisations were also urged to restrict access to sensitive systems according to employees’ responsibilities, regularly review privileged accounts and remove access when it is no longer required.
The presentation warned that outdated software, unsupported systems, weak configurations, exposed remote-access services and inadequately protected backups could create opportunities for attackers.
It also discouraged employees from bypassing security controls for convenience, installing unapproved software, sharing credentials to save time or sending sensitive files through unauthorised channels. Where security controls interfere with legitimate work, employees were advised to seek authorised support rather than create unofficial workarounds.
The bank’s presentation further urged employees to report suspected incidents promptly. These include clicking suspicious links, opening unexpected attachments, sending information to the wrong recipient, approving unauthorised authentication requests and noticing unusual account activity.
Employees were advised to stop the affected activity, report the incident through approved cybersecurity channels, preserve relevant information and follow instructions from authorised incident responders.
During the question-and-answer session, Dr. Olufemi Obadare, associate director and chief project manager at Digital Encode Limited, who addressed participants on employee security practices, urged workers to make cybersecurity awareness a continuous activity rather than treating it as a one-off exercise.
Obadare advised employees to pause and assess requests before acting, particularly as cybercriminals continue to change their tactics and exploit emerging technologies.
The webinar concluded with a call for employees, management, developers, system owners and business partners to make cybersecurity and data protection part of their everyday responsibilities. It also encouraged organisations to address security weaknesses, hold employees and partners accountable, and learn from incidents to improve their defences.
The central message was that protecting information requires more than deploying security technologies. It also depends on responsible employee behaviour, appropriate controls and the careful use of AI tools when handling sensitive information.




Human rights activist Maduabuchi Idam has said the promise by the Minister of Works, Dave Umahi, to deliver Ebonyi State to President Bola Tinubu in 2027 is a political ruse.
Idam likened Umahi's promise to an empty barrel of a gun making noise without shooting.
In a statement he signed, the constitutional lawyer said Umahi and the state governor, Francis Nwifuru, should provide functional healthcare facilities and electricity across the state before making such promises.
According to Idam: "The promise of delivering Ebonyi State to President Tinubu is a political ruse, almost like an empty-barrelled gun that makes a loud noise without firing a shot.
"There is no convincing dividend of governance to justify such an expectation. No one sings the Lord’s song in a strange land.
"Umahi and Nwifuru should begin by providing functional primary healthcare facilities and addressing the persistent electricity challenges in Afikpo and other communities across Ebonyi State.
"Governance must first be felt by the people before political loyalty in the form of votes can reasonably be demanded of them.
'Otherwise, the disappointment at the polls may be louder than the chants in the stadium.
"Amasiri needs a functional primary healthcare centre and the release of its people who are being maliciously prosecuted, while Afikpo in general needs a reliable electricity supply."
2027: Umahi, Nwifuru’s promise to deliver Ebonyi political ruse – Lawyer to Tinubu
News
Our Country Is Not Dead’ — Sunday Oliseh Hails World Cup-Winning Flamingos, Warns NFF Against Making Dangerous Mistake With Golden Generation

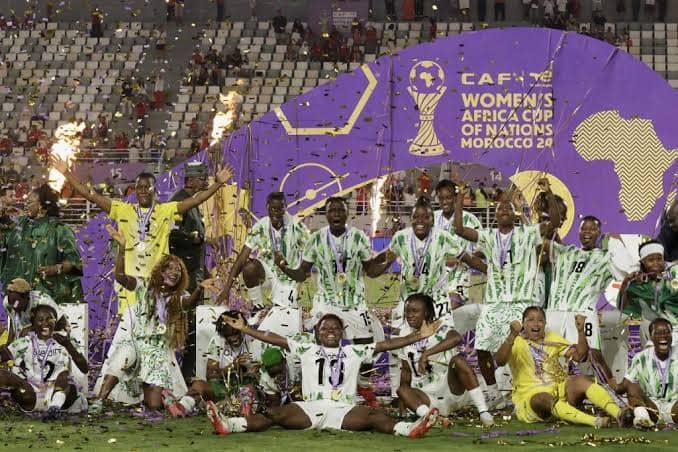
Former Super Eagles captain and head coach Sunday Oliseh has celebrated Nigeria’s historic FIFA U-17 Women’s World Cup triumph, declaring that the Flamingos’ remarkable achievement has proved that the country still possesses exceptional football talent, while warning the Nigeria Football Federation against restricting the development of the victorious youngsters, Sports247.ng reports.
Oliseh expressed particular satisfaction that many members of the World Cup-winning squad emerged from Nigeria’s domestic football system, describing their success as a powerful response to those who have repeatedly questioned the quality of home-based players.
The former Nigerian international insisted that the Flamingos’ achievement must become a turning point for grassroots football development rather than merely another moment of national celebration.
“Those who say, ‘Sunday, they always shout home-based, home-based.’ No, no, no. See them now, these ones are home-based. So we still get quality. Our country is not dead,” Oliseh declared.
The former Borussia Dortmund and Juventus midfielder stressed that the players’ achievement should receive sustained publicity to inspire other talented youngsters across the country.
“The multiplier effect now is like, it has to be publicised. For those who are following, let’s let them know what these girls have done. They’ve shown talent,” he explained.
However, Oliseh warned that Nigeria must avoid making the mistake of concentrating exclusively on the victorious squad without creating opportunities for other promising players.
According to him, keeping the World Cup winners together is important, but the NFF must simultaneously strengthen the team by introducing fresh talents.
“You can’t say, ‘Let’s keep them together.’ No. You have to try to keep them together, but you have to now integrate more, more,” he stated.
“If you keep them together, you create an elitist group. Keep them together, but you have to add more.”
Oliseh believes this approach would allow the achievements and experience of the World Cup champions to positively influence other emerging players, creating a stronger foundation for Nigeria’s future women’s national teams.
The former Super Eagles captain also emphasised that developing a successful football structure should involve more than celebrating one generation of players.
For Oliseh, the challenge is ensuring that Nigeria builds on the Flamingos’ achievement by identifying additional talents and creating a pathway for their progression through the national-team system.
Nigeria defeated Japan 2-1 in the final in Morocco, becoming the first African nation to win the FIFA U-17 Women’s World Cup.
While Nigerians continue celebrating the historic achievement, Oliseh’s message to football administrators is unmistakable: preserve the winning foundation, open the door to new talents and ensure that the Flamingos’ success becomes the beginning of something even greater.
-

 News3 days ago
Troops Arrest Suspected Gunrunner, Neutralise Two Terrorists in Plateau
-
News4 days ago
Makinde Visits COCIN Headquarters in Jos, Urges Christians to Shape Nigeria’s Political Future
-
News3 days ago
Makinde Unveils Four-Pillar Agenda to Reset Nigeria, Advocates State Police and National Unity Government
-
News2 days ago
APM holds Presidential Campaign in Plateau, Pledges Security and Economic Reset